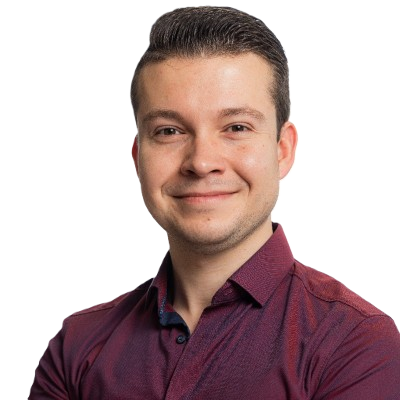
I'm Jordy Lok, an Information Security Officer and cybersecurity consultant with more than ten years in IT. My work sits where strategy meets the command line: translating board-level risk and compliance priorities into roadmaps engineers can actually execute, and staying hands-on enough to build the tooling myself.
This site is where I think out loud. Expect long-form writing on security leadership, governance and compliance, AI engineering and AI security, and the software engineering that holds it all together. Opinions are my own and not those of any employer or client.
What I work on
- Security strategy and governance: ISO 27001, NIS2, risk management and security programmes that survive contact with reality.
- AI security and compliance: threat modelling LLM systems, guardrails, and the EU AI Act.
- Cloud and platform security: AWS, Kubernetes, Terraform and DevSecOps pipelines.
- Incident response: DFIR, threat intelligence and the tooling that makes both faster.
Background
- Cybersecurity Consultant & Compliance Officer, ACA IT-Solutions (2024 to present)
- Cyber Security Lead, APS Group (2023 to 2024)
- Platform Engineer (Security), APS Group (2020 to 2024)
- IT Infrastructure Engineer, Osudio (2018 to 2020)
Certifications
CISSP, CCSP, EC-Council C|CISO, ISO/IEC 27001:2022 Lead Auditor, and AWS Architecting on AWS.
Experience
- Oct 2026 – PresentFounderValystrum
Valystrum, an AI-powered Continuous Assurance platform that connects compliance controls, evidence, cyber risk and live security signals.
- Mar 2025 – PresentCompliance OfficerACA IT-Solutions BV
- Feb 2025 – PresentChief Information Security Officer a.i (Via ACA IT-Solutions)KLG Europe
As interim CISO for IT Security & Compliance, I collaborate with cross-functional teams to ensure alignment with Information Security requirements across the organization. I provide strategic guidance on technical security measures, oversee compliance with regulatory standards, and drive initiatives to strengthen their security posture. Additionally, I advise and report to the C-level board on emerging risks, security needs, and investment priorities to support business objectives.
- Apr 2024 – PresentCybersecurity ConsultantACA IT-Solutions BV
As a Cybersecurity Consultant at Crowe IT Solutions, I guide and support organizations in strengthening their digital resilience and safeguarding the reliability of their information systems, ensuring business continuity in an increasingly complex threat landscape. Key Responsibilities: - Advising organizations of all sizes, from enterprises to government and healthcare, on improving their cybersecurity posture and aligning security with business objectives. - Conducting security audits and assessments, covering both technical infrastructure (e.g., network, endpoint, cloud, application security) and policy-level controls (e.g., governance, procedures, compliance). - Performing ad-hoc audits, recurring annual assessments, interim security officer roles, and in-depth security investigations. - Designing and implementing preventive, detective, and corrective security measures, including offensive security techniques such as vulnerability scanning and penetration testing. - Supporting technical hardening efforts by coaching IT administrators and guiding secure configuration of systems, services, and platforms. - Identifying and reporting technical vulnerabilities through coordinated disclosure and bug bounty programs. - Leading IT-security process improvement initiatives and conducting security research to inform strategic decisions. Applying and tailoring security frameworks such as: - CIS Controls - ISO/IEC 27001 & NEN7510-based ISMS - ISO/IEC 27002/27005-based risk management methodologies Translating complex security concepts into actionable insights for business stakeholders, bridging the gap between technical risks and strategic priorities.
- Jul 2024 – PresentPrivacy & Security Officer a.i. (Via ACA IT-Solutions)Wooninc. · Eindhoven, Noord-Brabant, Nederland
Advising, coordinating, and supporting the organization in enhancing security and privacy measures in accordance with BIC (Baseline Informatiebeveiliging voor Woningcorporaties) standards. This role involves providing guidance, ensuring effective coordination, and delivering ongoing support to help the organization strengthen its security and privacy protocols, ensuring compliance with the BIC (Baseline Information Security) framework both technically and compliance based.
- Mar 2026 – PresentPortfolioCyberShapers.io
Portfolio website
- Jul 2024 – Nov 2024Security Auditor (Via ACA IT-Solutions)Pallieter Group B.V. · Nederland
Continuous security audit processes for multiple subsidiaries, where I assess security both technically and at the policy level, and deliver reports based on security frameworks. This is to support the company in achieving its business objectives and to safeguard continuity for ongoing improvement.
- Dec 2023 – Mar 2024Cyber Security LeadAPS Group · Eindhoven, North Brabant, Netherlands
Transitioned into a Cyber Security Lead role to enhance organizational security posture, oversee vendor relationships, and drive compliance across IT operations. Key Responsibilities: - Vendor Relationship Management: Maintained secure and competitive vendor relationships, ensuring adherence to security standards. - Security Oversight: Defined boundaries and responsibilities to ensure comprehensive security coverage. - Stakeholder Communication: Regularly communicated security progress and issues to facilitate informed decision-making. - Task Planning and Execution: Planned and executed security tasks with clear deadlines and priorities. - Collaboration and Coordination: Worked with internal and external stakeholders to fulfill security requirements. - Information Dissemination: Established methodologies for sharing security-related updates with stakeholders. - Security Testing Oversight: Directed security tests to ensure systems met stringent standards. - Proposal Evaluation: Assessed bids to ensure alignment with security needs. - Gap Resolution: Managed security vulnerabilities to ensure swift resolution. - Procurement Security: Oversaw secure procurement processes to mitigate risks. - Change Management: Implemented secure IT environment changes in compliance with protocols. - Documentation and Review: Maintained evidence of compliance for external reviews. Key Achievements: - Strengthened security with real-time monitoring and compliance checks. - Championed a DevSecOps culture, integrating security into development. - Improved vendor relationships and standardized security practices across the business. Technical Expertise: - Tools: Terraform, Ansible, Jenkins, GitLab CI/CD, Docker, Kubernetes. - Cloud: AWS (EC2, S3, RDS, Lambda, IAM, VPC). - Security: Identity Management, Compliance Automation. - Languages: Python, Bash. - Methodologies: Agile, Scrum.
- Jul 2020 – Mar 2024Platform Engineer (Security)APS Group · Eindhoven, Noord-Brabant, Nederland
Empowered development and operations teams to deliver faster and more reliably by leveraging automation and cloud-native technologies. Built a secure, scalable platform aligned with organizational goals and a cloud-first strategy. Key Responsibilities: - Automated infrastructure with Terraform, enabling repeatable, scalable deployments. - Developed CI/CD pipelines, reducing deployment time and improving efficiency. - Configured systems with Ansible to ensure consistency and minimize manual errors. - Deployed and managed containerized apps with Kubernetes, enhancing scalability. - Enforced AWS Cloud Security best practices, protecting sensitive data. - Led AWS cloud deployments, prioritizing reliability and cost-effectiveness. - Integrated hybrid cloud environments for seamless operations. - Advised on security and compliance, driving regulatory adherence. - Facilitated collaboration to improve feedback loops and delivery quality. Key Achievements: - Delivered a security scalable cloud-first platform, reducing operational overhead. - Strengthened security with real-time monitoring and compliance checks. - Fostered a DevSecOps culture, integrating security into development. Technical Expertise: - Tools: Terraform, Ansible, Jenkins, GitLab CI/CD, Docker, Kubernetes. - Cloud: AWS (EC2, S3, RDS, Lambda, IAM, VPC). - Security: Identity Management, Compliance Automation. - Languages: Python, Bash. - Methodologies: Agile, Scrum.
- Mar 2018 – Jun 2020Information Technology Infrastructure EngineerOsudio · Eindhoven, Amsterdam, Dortmund (Germany) & Diepenbeek (Belgium)
In my role at Osudio, I developed a strong foundation in Routing & Switching at a CCNA level and expanded my technical expertise across several domains. I managed both Windows and Linux servers, automated Linux systems with Puppet, and oversaw Office 365 and Atlassian environments like Jira and Confluence. Additionally, I handled CI/CD pipelines with tools such as Nexus, Sonar, GitLab, and Kubernetes. I also administered web technologies, including Apache, Varnish, and NGINX, and was responsible for Docker, Kubernetes, and Xen Hypervisor management. As the VOIP administrator, I worked extensively with Asterisk (versions 13 & 16), providing crucial support and ongoing maintenance. During my time there, I tackled complex troubleshooting, created and maintained thorough documentation, and ensured accurate CMDB records. My role also involved performing security testing for client web services and successfully leading a major infrastructure migration from an external datacenter to an internal private cloud. One of the highlights of this position was the opportunity to share my knowledge with the team, offering coaching and support to ensure everyone adhered to best practices. I maintained SLA commitments, handled various local IT issues, and ensured smooth network and system operations through continuous monitoring and maintenance.
- Jun 2016 – Feb 2018Junior System Application consultant/administrator & Intern supervisorUnlimited Footwear Group · Waalwijk
Summary: System application and system consultant and administrator across multiple co-locations in the Netherlands. Proficient in providing exceptional customer service, managing workplace environments. Skilled in diverse areas including network administration, VoIP management, Office 365 implementation, Windows migration, ERP system operations, SQL Server management, and financial systems administration. Key Competencies: Customer-Centric Approach: Adept at delivering exceptional customer care by addressing IT-related issues promptly and effectively, ensuring high satisfaction levels. - Technical Expertise: Proficient in Routing and Switching (CCNA Level) and VoIP management (Broadsoft), providing stable and reliable network connectivity and communication solutions. - Project Management: Experienced in managing end-to-end IT projects, from requirement gathering and documentation to successful execution, ensuring on-time delivery and stakeholder satisfaction. - Microsoft Technologies: Skilled in implementing, configuring, and managing Office 365 environments, optimizing productivity and collaboration. - Migration and Training: Successful track record in executing Windows 10 migration projects, coupled with comprehensive training programs for seamless user adoption. - ERP Operations: Accomplished in overseeing ERP LN system operations, from administration and maintenance to monitoring, ensuring smooth business operations. - Database Management: Proficient in SQL Server administration, performing routine maintenance and monitoring to ensure data integrity and accessibility. - Server Administration: Experienced in managing Windows Server environments (2008 R2, 2012 R2, 2016), maintaining security, stability, and performance. - Financial System Administration: Skilled in managing and maintaining financial systems using d-Basics, ensuring accurate and secure financial data management.
- Oct 2014 – Jun 2016Field Services EngineerStudentaanhuis.nl · Drunen, North Brabant, Netherlands
On-site support and computer training in several areas of installation, support and training about home and small-business IT equipment and software. Keywords: networking, software, recovery
- Dec 2013 – Nov 2015Administrative AssistantSwiss Sense · Uden
National packet service
- Jan 2014 – Jun 2014Help Desk TechnicianAvans Hogeschool · 's Hertogenbosch
Responsible for first, second and third-line IT support for a school with almost 30k students. Project lead for several migration topics - Windows 7 -> 8.1 - Office2007/10 -> Office2013
- Aug 2012 – Jan 2013Help Desk InternSoftware Society · Drunen
Helpdesk technician and customer-care & advisor
- Jun 2011 – Jun 2012Customer Service Representative & IT TechnicianPriest Computers · Waalwijk
Customer care & advisor and IT technician for support and assembling bespoke computers
Education
- Sep 2024 – Sep 2024OptiSec Cyber Security TrainingenISC2 Certified Information System Security Professional (CISSP)
- Nov 2022 – Dec 2022Security AcademyISC² Certified Cloud Security Professional (CCSP)
- Hogeschool UtrechtBachelorgraad
- Koning Willem 1 CollegeMBO Niveau 4
- 'd OultremontcollegeVMBO-Kader
- 2019 – PresentCisco Networking AcademyNetaCad Student
Licences & certifications
- Sep 2012ECDL Office 2010Koning Willem I College
- Mar 2015MBO Niveau 4 - ICT-BeheerderKoning Willem I College
- Apollo 13Koning Willem I College
- Jun 2008VMBO Kader ICT-Routed'Oultremontcollege
- May 2017Deployment options for MacPluralsight
- May 2017Updates and Downloads for MacPluralsight
- May 2017Profile Manager for MacPluralsight
- May 2017NetRestore and NetInstall for MacPluralsight
- May 2017Management Options for MacPluralsight
- May 2017Installation Images for MacPluralsight
- Mar 2018AWS Cloud Practitioner EssentialsAmazon Web Services
- Mar 2019IT Security awarenessSQLI
- May 2020NSE 1 Network Security AssociateFortinet
- Aug 2020CPD - Equality and DiversityAPS Group
- Nov 2020Architecting on AWSAmazon Web Services (AWS)
- Jun 2021CPD - General Data Protection RegulationAPS Group
- Jun 2021CPD - Information Security SuiteAPS Group
- Sep 2022AWS Technical EssentialsAmazon Web Services (AWS)
- Sep 2022(ISC)² Candidate(ISC)²
- Oct 2022Migrating to AWSAmazon Web Services (AWS)
- Nov 2022AWS Well-Architected Best PracticesAmazon Web Services (AWS)
- Aug 2023Associate of (ISC)²(ISC)²
- Aug 2023
- Oct 2023The changing role of the CISO 2.0SECO-Institute
- Sep 2023
- Dec 2023Advanced AWS Well-Architected Best PracticesAmazon Web Services (AWS)
- Jan 2024What, Why, Who, and How of Cybersecurity StrategyISC2
- Jan 2024Zero Trust Architecture in the CloudISC2
- Jun 2024
- Nov 2024
- Jan 2025Associate Certified Chief Information Security Officer (C|CISO)EC-Council
- Nov 2025ISO/IEC 27001:2022 Lead AuditorMastermind
Skills
- Cyber threat intelligence (CTI)
- Informatiebeveiliging
- Informatieveiligheid
- Internetbeveiliging
- Entrepreneurship
- Compliance Automation
- DevSecOps
- AI Governance
- Security Strategy
- Blogger
- Cyber defense
- Artifical intelligence
- Digital forensics
- Strategic Leadership
- Strategisch leiderschap
- Identity & Access Management (IAM)
- Asset security
- Communication strategy
- Risk management
- Security assessment
- Security engineering
- Security operations
- Software development security
- IT-security assessments
- Business continuity
- Consultancy
- Leadership
- Avg
- Gdpr
- Data Security
- Cyber security
- Microsoft Security
- Windows
- Cyber Security management
- Cyber Risk Management
- Information Security Management
- Security Management
- Cloud Platform Security
- Cloud Design
- Cloud Infrastructure Security
- Cloud Legal Requirements
- Cloud Compliance
- Cloud Operations
- Cloud Data Security
- Cloud Application Security
- Cloud Architectural Concepts
- Networking
- Project Management
- Server Administration
- Voice over IP (VoIP)
- Cloud Computing
- Compliance
- Compliancemanagement
- Penetration Testing
- Amazon Web Services (AWS)
- Security
- Software Development
- Terraform
- Kubernetes
- DevOps
- Network Security
- Cloud Security
- Information Security
- Security Incident Response
- Computerbeveiliging
- IT Infrastructure Management
- Network Engineering
- Wireless Networking
- Probleemoplossing
- Cisco-technologie
- Windows server 2008 R2
- Android
- Microsoft SQL-server
- Linux
- Servers
- Customer Service
- Teamwork
- Browsers
- Network Monitoring Tools
On LinkedIn
Jordy Lok
Founder @ Valystrum | AI-powered Continuous Assurance platform that connects compliance controls, evidence, cyber risk and live security signals.
I’m the founder of Valystrum, building an AI-powered Continuous Assurance platform for ISO 27001, NIS2, GRC and cloud security. Connecting compliance evidence with real-world cyber risk.Most organisations still manage controls, audits, risks and technical findings in separate tools. Valystrum brings controls, evidence, risk, cloud posture and live security signals together so teams can move from point-in-time compliance to continuously demonstrable security.Alongside building Valystrum, I work as a Cybersecurity Consultant at Crowe. With 10+ years in IT, I’ve worked across platform engineering, cloud security, governance and hands-on security delivery. That background helps me translate C-level risk and regulatory priorities into measurable controls, practical roadmaps and technical improvements that teams can actually implement.My core areas include:• Cybersecurity strategy, GRC and risk management• ISO 27001, NIS2 and security compliance• DevSecOps, secure design and security automation• Vulnerability management, penetration testing and incident response• C-level advisory, board reporting and stakeholder alignmentI’m most effective where governance meets engineering: discussing risk appetite, regulatory exposure and security investment with leadership, then working with technical teams on identity, cloud posture, architecture, findings and remediation.My certifications include CISSP, CCSP, C|CISO, ISO 27001 Lead Auditor and multiple AWS certifications. I keep my technical skills current through labs, assessments and building real security products.I share practical lessons on Continuous Assurance, GRC, ISO 27001, NIS2, cloud security, AI governance and building Valystrum.For design partnerships, security collaboration or relevant founder conversations, send me a LinkedIn message or an email on [email protected]
Company pageValystrum
Continuous assurance for cyber risk, compliance and security operations.
Valystrum is an AI-powered Continuous Assurance platform that connects compliance controls, evidence, cyber risk and live security signals. The platform brings GRC, continuous control monitoring, cloud posture, attack-surface management, vulnerability intelligence, third-party risk and remediation into one operational environment. By connecting governance requirements with real technical signals, Valystrum helps organisations move beyond point-in-time assessments and maintain continuously demonstrable security. Valystrum supports organisations working with requirements and frameworks including ISO 27001, NIS2, NIST CSF, CIS Controls, SOC 2, DORA, GDPR, NEN 7510, ISO 42001 and the EU AI Act. Valystrum is designed for cloud-driven organisations, regulated businesses and security service providers that need a clearer connection between compliance, risk and technical security operations. Valystrum is developed and operated by Valystrum B.V., part of Valystrum Group B.V.